IPv6 exists because the 32-bit IPv4 address space ran out: roughly 4.3 billion addresses was never going to cover the modern internet. IPv6 uses 128-bit addresses, which is an almost unimaginably larger pool, but the size is not the part that trips people up. What trips people up is the five address types that all look similar and the EUI-64 math that turns a MAC address into an interface ID. This guide covers the address format, how to identify any address by type, what each type is for, the EUI-64 process worked out against real router output, and how to configure IPv6 on a Cisco router.
Checked again on two GNS3 c7200 routers running IOS 15.2 in October 2026, and the SLAAC and duplicate-address output further down comes straight from that run.
This guide assumes you are comfortable with IPv4 addressing and prefix notation; if not, the subnetting primer covers the /n prefix idea that carries straight over to IPv6.
What an IPv6 address looks like
An IPv6 address is 128 bits, written as eight groups of four hexadecimal digits separated by colons. Written in full, an address is long, so two abbreviation rules shorten it. First, drop the leading zeros in any group. Second, replace the single longest run of consecutive all-zero groups with a double colon (::), which may appear only once in an address. The key insight is that :: can appear once because a parser fills it back out by counting the groups on either side; allow it twice and the length becomes ambiguous.
The same address, written long and then short:
| Form | Address |
|---|---|
| Full | 2001:0DB8:0000:0001:0000:0000:0000:0001 |
| Leading zeros dropped | 2001:DB8:0:1:0:0:0:1 |
| Longest zero run as :: | 2001:DB8:0:1::1 |
Prefix length works exactly as in IPv4: a /n after the address marks how many leading bits are the network portion. For LAN subnets that value is almost always /64, which splits the address into a 64-bit network half and a 64-bit host (interface) half.
How to identify an IPv6 address by its first digits
The type of an IPv6 address is decided by its first digit or two, so identification is a lookup, not a calculation. This is the table worth keeping in your head:
| First digits | Address type | Routability | Notes |
|---|---|---|---|
| 2 or 3 | Global unicast | Internet-routable | Assigned by an ISP or RIR (2000::/3) |
| FD | Unique local | Site only, not on the internet | The RFC 1918 of IPv6 |
| FE80 | Link-local | One link only, never forwarded | Auto-generated on every interface |
| FF | Multicast | Scope-dependent | Replaces broadcast; no unicast use |
| FC | Unique local (reserved) | None today | Officially reserved, not deployed |
Anycast is the exception: it has no prefix of its own. An anycast address looks identical to a global unicast or unique local address, and the only difference is administrative, covered below.
Global unicast addresses
A global unicast address (GUA) is the IPv6 equivalent of a public IPv4 address: globally unique and routable on the internet. It starts with a 2 or 3 (the 2000::/3 block). What’s actually happening inside a GUA is a three-part split. The first 48 bits are the Global Routing Prefix your ISP or regional registry assigns. The next 16 bits are a Subnet ID you control, enough for 65,536 subnets. The last 64 bits are the Interface ID, the host part.
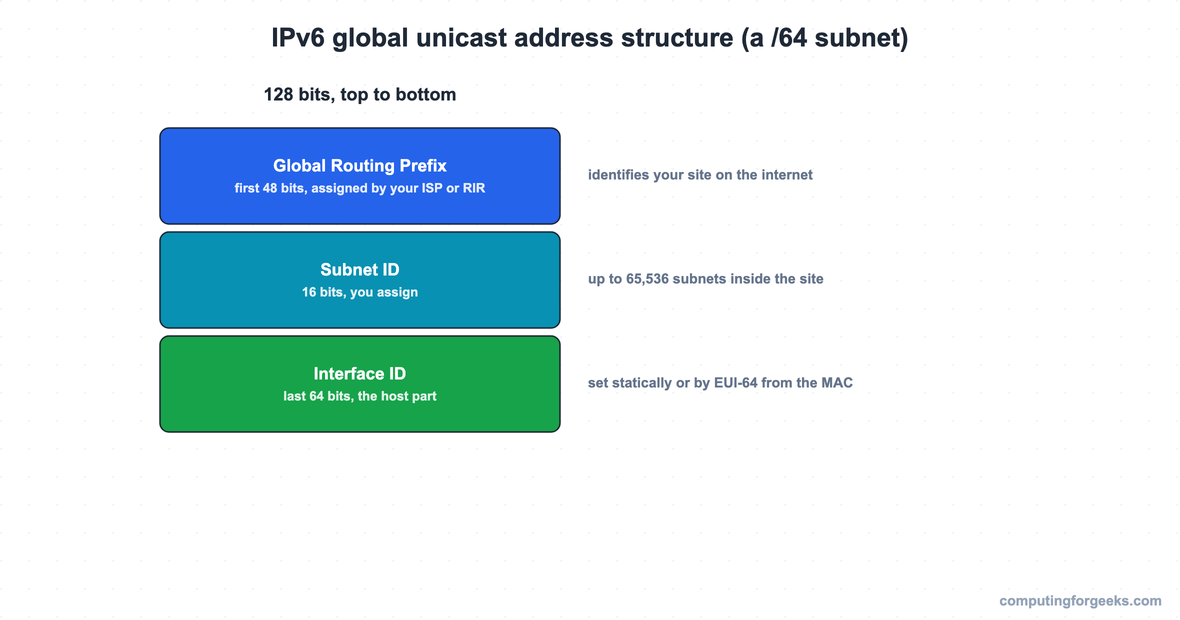
The 64-bit boundary matters because it is where the host part begins, and it is the line that EUI-64 and stateless autoconfiguration both work against. A site that receives a /48 from its ISP has 16 subnet bits to carve /64 networks from, which is the standard enterprise layout. The carving is the same binary exercise as variable-length subnetting in IPv4, only with so many bits that you rarely subnet below /64.
Unique local addresses
Unique local addresses (ULAs) are the RFC 1918 of IPv6: usable inside a site, never routed on the public internet. In practice they always begin with FD. The standard reserves the wider FC00::/7 block, but RFC 4193 requires a bit that forces the second hex digit to D, so a real ULA is always FD; FC is reserved and unused. After the FD comes a 40-bit Global ID that you are meant to generate randomly, which is what keeps two organizations from colliding when they merge networks that both use internal IPv6. A ULA looks like FD3A:91C4:7E05:1::1/64 (yours should come from your own random Global ID), and you configure it exactly like a GUA.
Link-local addresses and the EUI-64 process
Every IPv6-enabled interface gets a link-local address automatically, with no configuration, the moment IPv6 is active on it. Link-local addresses always begin FE80 and are never forwarded past the local link. They are not a curiosity: the mechanism that discovers a neighbor’s MAC (NDP, the IPv6 replacement for ARP) runs over link-local, routing protocols form neighbor adjacencies over link-local, and the next hop of a route learned from a routing protocol is a link-local address, not a global one (a static route can still point at a global next hop, as the IPv6 static routes guide shows). That last point surprises people the first time they read show ipv6 route: the next hop they expected to be a global address is an FE80 one, because link-local addresses never change even when the global prefix does.
Cisco IOS builds the interface ID for that link-local address with modified EUI-64, a four-step process that turns a 48-bit MAC into a 64-bit interface ID. Worked out against the lab router’s MAC of 0201.ABCD.0001:
| Step | Action | Result |
|---|---|---|
| 1 | Start with the 48-bit MAC (12 hex digits) | 0201.ABCD.0001 |
| 2 | Split it into two 24-bit halves | 0201AB and CD0001 |
| 3 | Insert FFFE between the halves | 0201:ABFF:FECD:0001 |
| 4 | Flip the 7th bit of the first byte (02 becomes 00) | 0001:ABFF:FECD:0001 |
The interface ID is 0001:ABFF:FECD:0001, so the link-local address is FE80::1:ABFF:FECD:1. The two giveaways that an address came from EUI-64 are the FF:FE sitting in the middle and the flipped 7th bit. The router output confirms the math exactly, on both the link-local and the EUI-64 global address.
The link-local and the global address both end in 1:ABFF:FECD:1, and the global address carries the [EUI] tag:
R1# show ipv6 interface GigabitEthernet0/0
GigabitEthernet0/0 is up, line protocol is up
  IPv6 is enabled, link-local address is FE80::1:ABFF:FECD:1
  No Virtual link-local address(es):
  Global unicast address(es):
    2001:DB8:CAFE:2:1:ABFF:FECD:1, subnet is 2001:DB8:CAFE:2::/64 [EUI]
  Joined group address(es):
    FF02::1
    FF02::2
    FF02::1:FFCD:1
  MTU is 1500 bytes
  ICMP error messages limited to one every 100 milliseconds
  ICMP redirects are enabled
  ICMP unreachables are sent
  ND DAD is enabled, number of DAD attempts: 1
  ND reachable time is 30000 milliseconds (using 30000)
  ND advertised reachable time is 0 (unspecified)
  ND advertised retransmit interval is 0 (unspecified)
  ND router advertisements are sent every 200 seconds
  ND router advertisements live for 1800 seconds
  ND advertised default router preference is Medium
  Hosts use stateless autoconfig for addresses.
Multicast addresses
IPv6 has no broadcast. Multicast does that job, and every multicast address begins with FF. The fourth hex digit encodes scope, which is how far the packet travels: FF02 is link-local scope (stays on the link), while FF0E is global. A handful of link-local multicast groups appear constantly and are worth memorizing.
| Address | Group |
|---|---|
| FF02::1 | All nodes on the link |
| FF02::2 | All routers on the link |
| FF02::5 | All OSPFv3 routers |
| FF02::6 | All OSPFv3 designated routers |
These are not theoretical. The show ipv6 interface capture above lists FF02::1 and FF02::2 under “Joined group address(es)”, alongside a solicited-node address (FF02::1:FFCD:1) that NDP derives from the interface’s own address to do efficient neighbor discovery.
Anycast addresses
An anycast address is one address assigned to several interfaces, usually on several routers. The network delivers a packet sent to that address to whichever holder is topologically nearest. There is no special prefix; an anycast address is drawn from the global unicast or unique local range and configured with an anycast keyword so the device knows not to treat duplicates as a conflict. The idea to hold onto is the concept rather than any configuration: same address, nearest node answers.
Configuring IPv6 on a Cisco router
The one command people forget is the first one. IPv6 routing is off by default on a Cisco router, the opposite of IPv4. A router with addresses configured still drops any IPv6 packet not destined to itself until you enable routing globally:
enable
configure terminal
ipv6 unicast-routing
interface GigabitEthernet0/0
mac-address 0201.ABCD.0001
ipv6 address 2001:DB8:CAFE:2::/64 eui-64
no shutdown
interface Loopback0
ipv6 address 2001:DB8:CAFE:1::1/64
end
The mac-address line is only there so the lab output matches the worked example: we set 0201.ABCD.0001 by hand (the 02 marks it as a locally administered address), and on your router the interface’s burned-in MAC produces a different interface ID. The eui-64 keyword tells IOS to build the interface ID from the MAC, as worked out above. To set the whole address by hand instead, give the full address and prefix: ipv6 address 2001:DB8:CAFE:1::1/64. Verify both forms with show ipv6 interface brief, which lists each interface with its automatic link-local address and its configured global address:
R1# show ipv6 interface brief
Ethernet0/0            [administratively down/down]
    unassigned
GigabitEthernet0/0     [up/up]
    FE80::1:ABFF:FECD:1
    2001:DB8:CAFE:2:1:ABFF:FECD:1
GigabitEthernet1/0     [administratively down/down]
    unassigned
GigabitEthernet2/0     [administratively down/down]
    unassigned
Loopback0              [up/up]
    FE80::C801:BCFF:FE60:6
    2001:DB8:CAFE:1::1
Each IPv6-enabled interface shows two addresses: the FE80 link-local that IOS generated on its own, and the global address you configured. That pairing, one automatic link-local and one routable global address per interface, is the normal IPv6 state, and it is the same workflow as the rest of the base device configuration.
The configured prefixes show up in the routing table either way; what ipv6 unicast-routing adds is forwarding between them. Running show ipv6 route connected on the lab router lists each configured /64 as a directly connected route, the 2001:DB8:CAFE:1::/64 and 2001:DB8:CAFE:2::/64 prefixes that the router can now forward between. Without ipv6 unicast-routing, those addresses still exist on the interfaces, but the router refuses to forward anything between them, which is the detail worth burning into memory. The output, with the route code legend trimmed:
R1# show ipv6 route connected
IPv6 Routing Table - default - 5 entries
C   2001:DB8:CAFE:1::/64 [0/0]
     via Loopback0, directly connected
C   2001:DB8:CAFE:2::/64 [0/0]
     via GigabitEthernet0/0, directly connected
Forwarding is only half of what that one command switches on. Until it is set, the router also sends no router advertisements, so hosts on the link can’t autoconfigure an address from it, which is easy to prove with a second router.
SLAAC and duplicate address detection on a real link
To watch stateless autoconfiguration (SLAAC) happen, we cabled two c7200 routers together and gave the link the prefix 2001:DB8:CAFE:12::/64. R1 holds 2001:DB8:CAFE:12::1/64 and plays the router. R2 plays a host: its Gi0/0 runs ipv6 enable and ipv6 address autoconfig, so it takes whatever prefix a router advertises. The interface MACs matter for the EUI-64 math later, so we read them first:
R1# show interfaces GigabitEthernet0/0 | include bia
  Hardware is i82543 (Livengood), address is ca01.0778.0008 (bia ca01.0778.0008)

R2# show interfaces GigabitEthernet0/0 | include bia
  Hardware is i82543 (Livengood), address is ca02.0794.0008 (bia ca02.0794.0008)
No router advertisements until unicast routing is on
This is a fresh two-router lab, separate from the one-router configuration above, so ipv6 unicast-routing starts off on R1. R1’s Gi0/0 carries only ipv6 address 2001:DB8:CAFE:12::1/64 and no shutdown; R2’s Gi0/0 carries ipv6 enable, ipv6 address autoconfig and no shutdown. With routing off on R1, R2 only ever got its link-local address. IOS says so plainly, and R2 has no router to list:
R2# show ipv6 interface GigabitEthernet0/0
GigabitEthernet0/0 is up, line protocol is up
  IPv6 is enabled, link-local address is FE80::C802:7FF:FE94:8
  No Virtual link-local address(es):
  Stateless address autoconfig enabled
  No global unicast address is configured
  Joined group address(es):
    FF02::1
    FF02::1:FF94:8
  MTU is 1500 bytes
  ICMP error messages limited to one every 100 milliseconds
  ICMP redirects are enabled
  ICMP unreachables are sent
  ND DAD is enabled, number of DAD attempts: 1
  ND reachable time is 30000 milliseconds (using 30000)
  ND NS retransmit interval is 1000 milliseconds

R2# show ipv6 routers
R1 isn’t acting as an IPv6 router at this point, and its own interface shows it: the joined groups include the all-nodes group FF02::1 but not the all-routers group FF02::2, and there are no RA lines:
R1# show ipv6 interface GigabitEthernet0/0
GigabitEthernet0/0 is up, line protocol is up
  IPv6 is enabled, link-local address is FE80::C801:7FF:FE78:8
  No Virtual link-local address(es):
  Global unicast address(es):
    2001:DB8:CAFE:12::1, subnet is 2001:DB8:CAFE:12::/64
  Joined group address(es):
    FF02::1
    FF02::1:FF00:1
    FF02::1:FF78:8
  MTU is 1500 bytes
  ICMP error messages limited to one every 100 milliseconds
  ICMP redirects are enabled
  ICMP unreachables are sent
  ND DAD is enabled, number of DAD attempts: 1
  ND reachable time is 30000 milliseconds (using 30000)
  ND NS retransmit interval is 1000 milliseconds
Enabling routing changes both:
R1# configure terminal
Enter configuration commands, one per line.  End with CNTL/Z.

R1(config)# ipv6 unicast-routing

R1(config)# end

R1# show ipv6 interface GigabitEthernet0/0
GigabitEthernet0/0 is up, line protocol is up
  IPv6 is enabled, link-local address is FE80::C801:7FF:FE78:8
  No Virtual link-local address(es):
  Global unicast address(es):
    2001:DB8:CAFE:12::1, subnet is 2001:DB8:CAFE:12::/64
  Joined group address(es):
    FF02::1
    FF02::2
    FF02::1:FF00:1
    FF02::1:FF78:8
  MTU is 1500 bytes
  ICMP error messages limited to one every 100 milliseconds
  ICMP redirects are enabled
  ICMP unreachables are sent
  ND DAD is enabled, number of DAD attempts: 1
  ND reachable time is 30000 milliseconds (using 30000)
  ND advertised reachable time is 0 (unspecified)
  ND advertised retransmit interval is 0 (unspecified)
  ND router advertisements are sent every 200 seconds
  ND router advertisements live for 1800 seconds
  ND advertised default router preference is Medium
  Hosts use stateless autoconfig for addresses.
R1 now listens on FF02::2 and advertises every 200 seconds. We didn’t shorten that interval, yet R2 had its address within the 40 seconds we waited, because a router that has just started advertising sends its first few RAs at intervals of no more than 16 seconds (RFC 4861); the lifetimes below show the RA had arrived about 14 seconds before the capture. R2’s address is built from the advertised prefix plus its own EUI-64 interface ID:
R2# show ipv6 interface brief
Ethernet0/0            [administratively down/down]
    unassigned
GigabitEthernet0/0     [up/up]
    FE80::C802:7FF:FE94:8
    2001:DB8:CAFE:12:C802:7FF:FE94:8
GigabitEthernet1/0     [administratively down/down]
    unassigned
GigabitEthernet2/0     [administratively down/down]
    unassigned

R2# show ipv6 interface GigabitEthernet0/0
GigabitEthernet0/0 is up, line protocol is up
  IPv6 is enabled, link-local address is FE80::C802:7FF:FE94:8
  No Virtual link-local address(es):
  Stateless address autoconfig enabled
  Global unicast address(es):
    2001:DB8:CAFE:12:C802:7FF:FE94:8, subnet is 2001:DB8:CAFE:12::/64 [EUI/CAL/PRE]
      valid lifetime 2591986 preferred lifetime 604786
  Joined group address(es):
    FF02::1
    FF02::1:FF94:8
  MTU is 1500 bytes
  ICMP error messages limited to one every 100 milliseconds
  ICMP redirects are enabled
  ICMP unreachables are sent
  ND DAD is enabled, number of DAD attempts: 1
  ND reachable time is 30000 milliseconds (using 30000)
  ND NS retransmit interval is 1000 milliseconds
  Default router is FE80::C801:7FF:FE78:8 on GigabitEthernet0/0
The [EUI/CAL/PRE] tag reads as EUI-64 interface ID, calendared (it has lifetimes from the RA) and preferred. The lifetimes count down from the advertised 30 days valid and 7 days preferred, and R2 also learned R1’s link-local address as its default router. show ipv6 routers shows the advertisement itself, and the routing table has picked up an ND default route without the default keyword on ipv6 address autoconfig. That works because R2 has ipv6 unicast-routing off, so IOS treats it as a host and takes its default router from the RAs; a router with routing enabled needs ipv6 address autoconfig default to install one (route code legend trimmed):
R2# show ipv6 routers
Router FE80::C801:7FF:FE78:8 on GigabitEthernet0/0, last update 0 min
  Hops 64, Lifetime 1800 sec, AddrFlag=0, OtherFlag=0, MTU=1500
  HomeAgentFlag=0, Preference=Medium
  Reachable time 0 (unspecified), Retransmit time 0 (unspecified)
  Prefix 2001:DB8:CAFE:12::/64 onlink autoconfig
    Valid lifetime 2592000, preferred lifetime 604800


R2# show ipv6 route
IPv6 Routing Table - default - 4 entries
ND  ::/0 [2/0]
     via FE80::C801:7FF:FE78:8, GigabitEthernet0/0
NDp 2001:DB8:CAFE:12::/64 [2/0]
     via GigabitEthernet0/0, directly connected
L   2001:DB8:CAFE:12:C802:7FF:FE94:8/128 [0/0]
     via GigabitEthernet0/0, receive
L   FF00::/8 [0/0]
     via Null0, receive
R2’s address is also a second chance to check the EUI-64 steps from earlier. Its MAC ca02.0794.0008 splits into ca0207 and 940008, FFFE goes in the middle to give ca02:07ff:fe94:0008, and flipping the 7th bit turns ca (1100 1010) into c8 (1100 1000). The interface ID is C802:7FF:FE94:8 once IOS drops the leading zeros, which is exactly what both of R2’s addresses end in.
Ping every node on the link with FF02::1
With no broadcast in IPv6, the all-nodes multicast group is how you check who is alive on a segment. IOS asks which interface to send a link-local multicast out of, and every IPv6 node on that link answers from its link-local address:
R1# ping FF02::1
Output Interface: GigabitEthernet0/0
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to FF02::1, timeout is 2 seconds:
Packet sent with a source address of FE80::C801:7FF:FE78:8%GigabitEthernet0/0

Reply to request 0 received from FE80::C802:7FF:FE94:8, 16 ms
Reply to request 1 received from FE80::C802:7FF:FE94:8, 16 ms
Reply to request 2 received from FE80::C802:7FF:FE94:8, 24 ms
Reply to request 3 received from FE80::C802:7FF:FE94:8, 12 ms
Reply to request 4 received from FE80::C802:7FF:FE94:8, 16 ms
Success rate is 100 percent (5/5), round-trip min/avg/max = 12/16/24 ms
5 multicast replies and 0 errors.

R1# show ipv6 neighbors
IPv6 Address                              Age Link-layer Addr State Interface
FE80::C802:7FF:FE94:8                       0 ca02.0794.0008  REACH Gi0/0
A reply also lands the sender in the neighbor cache with its MAC, which is the IPv6 replacement for an ARP entry. On a busy LAN the same ping returns one reply per host, so it doubles as a quick inventory.
%IPV6_ND-4-DUPLICATE: Duplicate address
Duplicate address detection (DAD) is why two devices can’t quietly share an IPv6 address. We configured R2 with 2001:DB8:CAFE:12::1/64, the address R1 already owns. R2 ran DAD before using the address, got an answer from R1, and logged the conflict:
R2# show logging | include IPV6
*Oct 14 09:22:52.635: %IPV6_ND-4-DUPLICATE: Duplicate address 2001:DB8:CAFE:12::1 on GigabitEthernet0/0
The trap is what the brief view does with that address. show ipv6 interface brief on R2 lists it like any working address, with no hint that it is unusable:
R2# show ipv6 interface brief
Ethernet0/0            [administratively down/down]
    unassigned
GigabitEthernet0/0     [up/up]
    FE80::C802:7FF:FE94:8
    2001:DB8:CAFE:12::1
    2001:DB8:CAFE:12:C802:7FF:FE94:8
GigabitEthernet1/0     [administratively down/down]
    unassigned
GigabitEthernet2/0     [administratively down/down]
    unassigned
Only the detailed view marks it [DUP], so when an address looks configured but nothing answers on it, check the full output:
R2# show ipv6 interface GigabitEthernet0/0
GigabitEthernet0/0 is up, line protocol is up
  IPv6 is enabled, link-local address is FE80::C802:7FF:FE94:8
  No Virtual link-local address(es):
  Stateless address autoconfig enabled
  Global unicast address(es):
    2001:DB8:CAFE:12::1, subnet is 2001:DB8:CAFE:12::/64 [DUP]
    2001:DB8:CAFE:12:C802:7FF:FE94:8, subnet is 2001:DB8:CAFE:12::/64 [EUI/CAL/PRE]
      valid lifetime 2591951 preferred lifetime 604751
  Joined group address(es):
    FF02::1
    FF02::1:FF94:8
  MTU is 1500 bytes
  ICMP error messages limited to one every 100 milliseconds
  ICMP redirects are enabled
  ICMP unreachables are sent
  ND DAD is enabled, number of DAD attempts: 1
  ND reachable time is 30000 milliseconds (using 30000)
  ND NS retransmit interval is 1000 milliseconds
  Default router is FE80::C801:7FF:FE78:8 on GigabitEthernet0/0
R1, which owns the address, logged only an informational message about the DAD attempt it saw:
R1# show logging | include IPV6
*Oct 14 09:22:53.047: %IPV6_ND-6-DUPLICATE_INFO: DAD attempt detected for 2001:DB8:CAFE:12::1 on GigabitEthernet0/0
To clear the conflict, go into interface configuration on R2 (interface GigabitEthernet0/0), remove the duplicate with no ipv6 address 2001:DB8:CAFE:12::1/64, and give the interface an address nobody else holds. The [DUP] address never becomes usable on its own, so leaving it configured only hides the problem.
Practice IPv6 addressing
Drill the address types, the first-digit identifiers, and the EUI-64 steps with the flashcards, then test yourself on the quiz. The deck is a downloadable Anki package for spaced repetition.
Now check what stuck:
Common IPv6 addressing misconceptions
Four ideas that carry over wrongly from IPv4 or from a quick skim of the address types.
Link-local addresses are not throwaway. An FE80 address looks like noise, but it is what neighbor discovery, routing adjacencies, and routing-table next hops actually use. You don’t have to configure it (though ipv6 address FE80::1 link-local lets you), and you never ignore it either.
The private prefix is FD, not FC. The standard reserves FC00::/7, so it is tempting to write a private address starting with FC. Real unique local addresses always start with FD; FC is reserved and not in use.
IPv6 does not need NAT to function. Unique local addresses give you private addressing, but the design intent is that every device can hold a real global address. NAT was an IPv4 workaround for scarcity, and IPv6 has no scarcity to work around.
The double colon is a one-time tool. :: compresses one run of zero groups per address. Using it twice makes the address ambiguous, so a parser rejects it. When two zero runs are equal length, compress the first. Get the address format and the five type prefixes solid, and the rest of IPv6 reads as routing and services layered on top of these same addresses. The CCNA 200-301 roadmap shows what comes next.