

Network Traffic Analysis (NTA) is the continuous process of capturing and analyzing network traffic to detect cyber threats, identify anomalous behavior and monitor network communications. It improves network visibility and supports effective security monitoring and incident response.
- Detects threats such as malware, unauthorized access, lateral movement, command-and-control (C2) communication and data exfiltration by analyzing network traffic.
- Analyzes network packets, flow records and logs to identify suspicious behavior, monitor network performance and support forensic investigations.
- Commonly used in enterprise networks, data centers and cloud environments for continuous network monitoring and threat detection.
Implementation of Network Traffic Analysis
Follow these essential steps to effectively monitor, analyze and secure your network traffic.
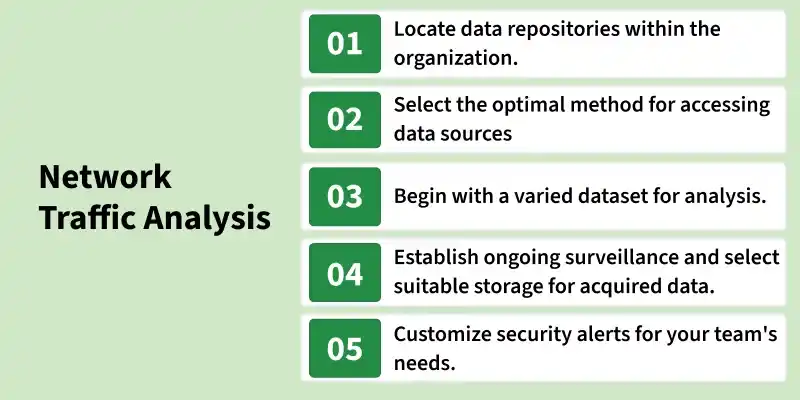
- Traffic Collection: Capture data using network taps, sensors or SPAN ports (packet or flow-based).
- Continuous Monitoring: Track traffic volume, protocols and communication patterns in real time.
- Pattern Analysis: Establish normal behavior (baseline) and identify deviations such as unusual IPs or ports.
- Threat Detection: Apply signatures, heuristics and machine learning models to detect malicious activity.
- Incident Response: Investigate alerts, block malicious traffic and strengthen defenses.
- Data Retention: Store logs and packet captures for forensic analysis, compliance and auditing.
Modern Trends in Network Traffic Analysis
Modern NTA has evolved beyond traditional monitoring and now includes:
- AI and Machine Learning: Automatically detect anomalies and unknown threats using behavioral analytics
- Network Detection and Response (NDR): Combines NTA with automated threat detection and response capabilities
- Cloud and Hybrid Visibility: Monitors traffic across on-premises, cloud and multi-cloud environments
- Zero Trust Integration: Supports strict access control by continuously validating network behavior
- Encrypted Traffic Analysis: Detects threats in encrypted traffic without full decryption
- East-West Traffic Monitoring: Tracks internal network movement to detect lateral attacks
Common Network Traffic Analysis Tools
These tools help security teams capture, analyze and monitor network traffic, detect intrusions and ensure optimal performance across the infrastructure.
- Packet Capture & Analysis: Wireshark, tcpdump, TShark.
- Intrusion Detection/Prevention Systems (IDS/IPS): Snort, Suricata.
- SIEM Platforms: Splunk, IBM QRadar, Microsoft Sentinel, ELK Stack (Elasticsearch, Logstash, Kibana).
- Network Performance Monitoring: SolarWinds, PRTG Network Monitor.
- Flow-Based Analysis: NetFlow Analyzer, SFlow/NetFlow collectors.
